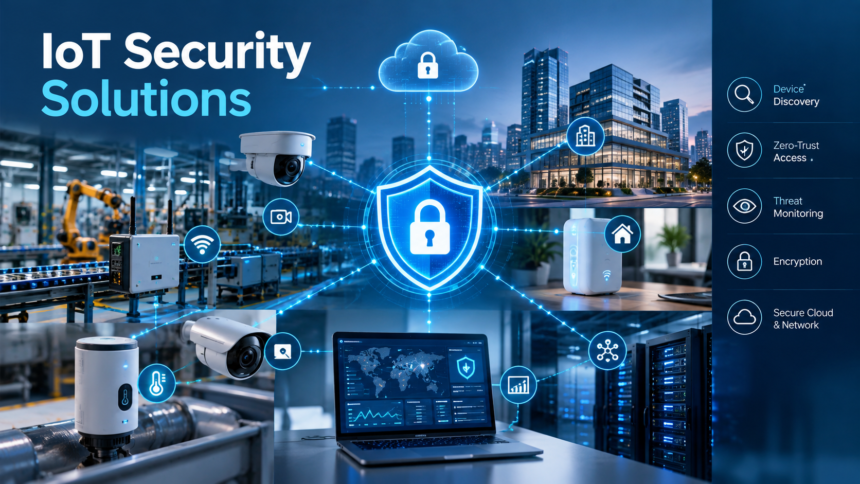
Connected devices now sit across offices, factories, healthcare environments, homes, vehicles, and critical infrastructure. That connectivity creates useful data and automation, but it also expands the number of systems that organizations must protect. IoT security solutions help reduce these risks by securing devices, communications, applications, cloud platforms, and the data moving between them.
Effective IoT security is not simply about installing antivirus software on a device. It involves identifying connected assets, controlling access, securing communications, managing updates, monitoring network activity, and planning for incidents. NIST and ENISA guidance both emphasize treating IoT security as part of broader organizational risk management and the full product lifecycle.
What Are IoT Security Solutions?
IoT security solutions are technologies, controls, and processes designed to protect Internet of Things environments from unauthorized access, malware, data exposure, device compromise, and other cyber threats.
An IoT environment can include sensors, cameras, industrial controllers, smart appliances, gateways, mobile applications, APIs, cloud services, and network infrastructure. Because these components interact, a weakness in one device can create consequences beyond that individual device.
A practical security strategy therefore considers the entire ecosystem rather than treating every connected device as an isolated endpoint. ENISA recommends security measures covering devices, communications, networks, cloud components, development, maintenance, and other stages of the IoT lifecycle.
Why IoT Security Requires a Different Approach
Traditional IT environments generally provide established mechanisms for identity management, patching, endpoint protection, and centralized administration. IoT environments can be more diverse. Some devices have limited processing resources, long operating lifetimes, proprietary software, or infrequent maintenance windows.
Organizations may also struggle to maintain an accurate inventory of every connected asset. An unknown camera, sensor, medical device, or industrial controller can become a security blind spot.
This makes visibility a fundamental requirement. NIST’s work on characterizing IoT network behavior highlights the importance of understanding which devices are present and what communications they actually require.
Key Components of IoT Security Solutions
A strong IoT security program normally combines several layers of protection rather than relying on a single product.
| Security area | What it protects | Practical approach |
|---|---|---|
| Device security | Hardware, firmware, and device credentials | Secure configuration, strong authentication, signed updates |
| Network security | Communications between devices and systems | Segmentation, firewalls, access controls, traffic monitoring |
| Data security | Sensitive information in transit and at rest | Encryption, access restrictions, secure storage |
| Identity and access | Devices, users, and applications | Least privilege, unique credentials, authentication |
| Monitoring | Suspicious behavior and anomalies | Logging, behavioral monitoring, alerting |
| Lifecycle management | Devices throughout their operational life | Inventory, patching, vulnerability management, secure disposal |
The objective is to create multiple defensive layers. If one control fails, another can limit the attacker’s ability to move further into the environment.
Device Authentication and Access Control
Weak or reused credentials remain a significant concern for connected environments. Devices should have unique identities and should not rely on unnecessary default passwords.
Access should also follow the principle of least privilege. A sensor that only needs to communicate with a specific application should not automatically have unrestricted access to internal servers.
Organizations evaluating iot security solutions should therefore examine how a platform handles device identity, authentication, authorization, credential management, and access policies.
For larger deployments, centralized identity and policy management can make it easier to apply consistent controls across thousands of devices.
Network Segmentation and Traffic Control
Network segmentation can reduce the potential impact of a compromised IoT device. Instead of placing cameras, smart appliances, employee computers, servers, and industrial equipment on one unrestricted network, organizations can separate them according to function and risk.
Traffic rules can then limit which systems are permitted to communicate.
NIST has demonstrated how Manufacturer Usage Description (MUD) can help restrict IoT devices to the network traffic they require for their intended functions. This approach can reduce exposure to certain network-based attacks and limit the potential damage from compromised devices.
💡 Pro Tip:
Before creating firewall rules, document what each IoT device actually needs to communicate with. Blocking unnecessary outbound connections can be more effective than creating broad rules based only on device type.
Encryption, Updates, and Secure Development
Encryption helps protect information as it travels between devices, gateways, applications, and cloud services. The appropriate implementation depends on the device, protocol, architecture, and sensitivity of the information involved.
Updates are equally important. Vendors should provide a practical mechanism for delivering security fixes, while organizations need processes for testing and deploying those updates without disrupting essential operations.
Security should also begin before deployment. ENISA’s IoT guidance emphasizes secure development practices across requirements, design, development, maintenance, and disposal rather than treating security as an afterthought.
For organizations selecting iot security solutions, support for vulnerability management, firmware updates, secure configuration, and lifecycle tracking can be as important as detection capabilities.
How to Choose IoT Security Solutions
The right approach depends on the organization’s environment, risk profile, device types, and operational requirements. A useful evaluation should consider:
- Asset visibility: Can the system discover and identify connected devices?
- Risk assessment: Can administrators prioritize vulnerable or high-risk assets?
- Authentication: Does it support strong device and user identity controls?
- Network controls: Can communication be restricted according to business requirements?
- Monitoring: Can suspicious behavior generate useful alerts?
- Integration: Can security data work with existing SIEM, firewall, endpoint, or cloud platforms?
- Lifecycle support: Does the solution address onboarding, maintenance, updates, and retirement?
- Scalability: Can it manage the expected number and variety of connected devices?
NIST’s IoT guidance recommends establishing cybersecurity requirements when organizations acquire and integrate IoT products, rather than waiting until after deployment.
Common IoT Security Mistakes
Several security weaknesses are caused by operational practices rather than sophisticated technical failures.
One common mistake is deploying devices without maintaining an accurate inventory. Another is leaving unnecessary services enabled or failing to change default credentials. Organizations can also overlook devices that are difficult to patch because they are embedded in larger operational systems.
A further problem is treating the vendor as the only party responsible for security. IoT security is shared across manufacturers, suppliers, integrators, network administrators, cloud providers, and device owners.
Supply-chain security deserves particular attention because components, software, and services may come from multiple organizations. ENISA recommends considering security throughout the IoT supply chain, from design and production through delivery, maintenance, and eventual disposal.
Building a Practical IoT Security Strategy
Organizations do not need to implement every control simultaneously. A structured approach can make improvement more manageable.
Start by identifying connected assets and classifying them according to their function and risk. Next, establish secure configurations, authentication requirements, network boundaries, and update procedures.
After deployment, monitor device behavior and investigate unexpected communication or configuration changes. Regularly review whether devices still require their existing access and whether unsupported equipment should be replaced.
For industrial environments, additional care may be necessary because cyber incidents can affect physical processes, production availability, equipment, or safety. ENISA’s Industry 4.0 guidance specifically addresses the cybersecurity challenges associated with industrial IoT environments.
📌 Key Takeaway:
Effective IoT protection comes from combining visibility, identity management, segmentation, secure communications, updates, monitoring, and lifecycle controls. The strongest iot security solutions are those that fit the organization’s actual devices, workflows, and risk requirements rather than relying on one security feature.
Frequently Asked Questions
What are IoT security solutions?
IoT security solutions are technologies and security practices used to protect connected devices, networks, applications, cloud services, and data. They can include device authentication, network segmentation, encryption, vulnerability management, monitoring, access controls, and secure update mechanisms.
Why is IoT security important for businesses?
IoT devices can connect physical environments to business networks and cloud systems. If poorly secured, a compromised device may provide an entry point into other resources or expose sensitive information. Security controls help organizations reduce unauthorized access, limit potential impact, and maintain reliable operations.
How can companies secure IoT devices?
Companies can begin with a complete device inventory, unique credentials, strong authentication, secure configurations, network segmentation, timely security updates, and continuous monitoring. They should also evaluate security requirements before purchasing new devices and establish processes for retiring unsupported equipment.
What should businesses look for in IoT security solutions?
Businesses should evaluate asset visibility, authentication, access control, network protection, monitoring, vulnerability management, integration capabilities, scalability, and lifecycle support. Requirements should reflect the organization’s devices, data, operational environment, regulatory obligations, and risk tolerance.
Can network segmentation protect IoT devices?
Network segmentation can reduce the exposure of IoT devices by restricting communication between device groups and other systems. It does not eliminate every risk, but carefully designed segmentation can limit unnecessary connectivity and help contain the effects of a compromised device.
Conclusion
IoT security is best treated as an ongoing lifecycle responsibility rather than a one-time deployment task. Devices need secure identities, controlled communications, timely updates, monitoring, and appropriate access throughout their operational lives. Organizations evaluating iot security solutions should begin with visibility and risk assessment, then build layered controls around the specific technologies and processes they need to protect.